What the verifier checks
- Recognize the issued tag or a protected tag reference.
- Validate the SDM message authentication code and any configured encrypted fields.
- Apply read-counter and replay policies appropriate to the application.
- Check issuance, revocation and product binding state.
- Return a defined authentication result and an auditable request reference where supported.
Reference integration flow
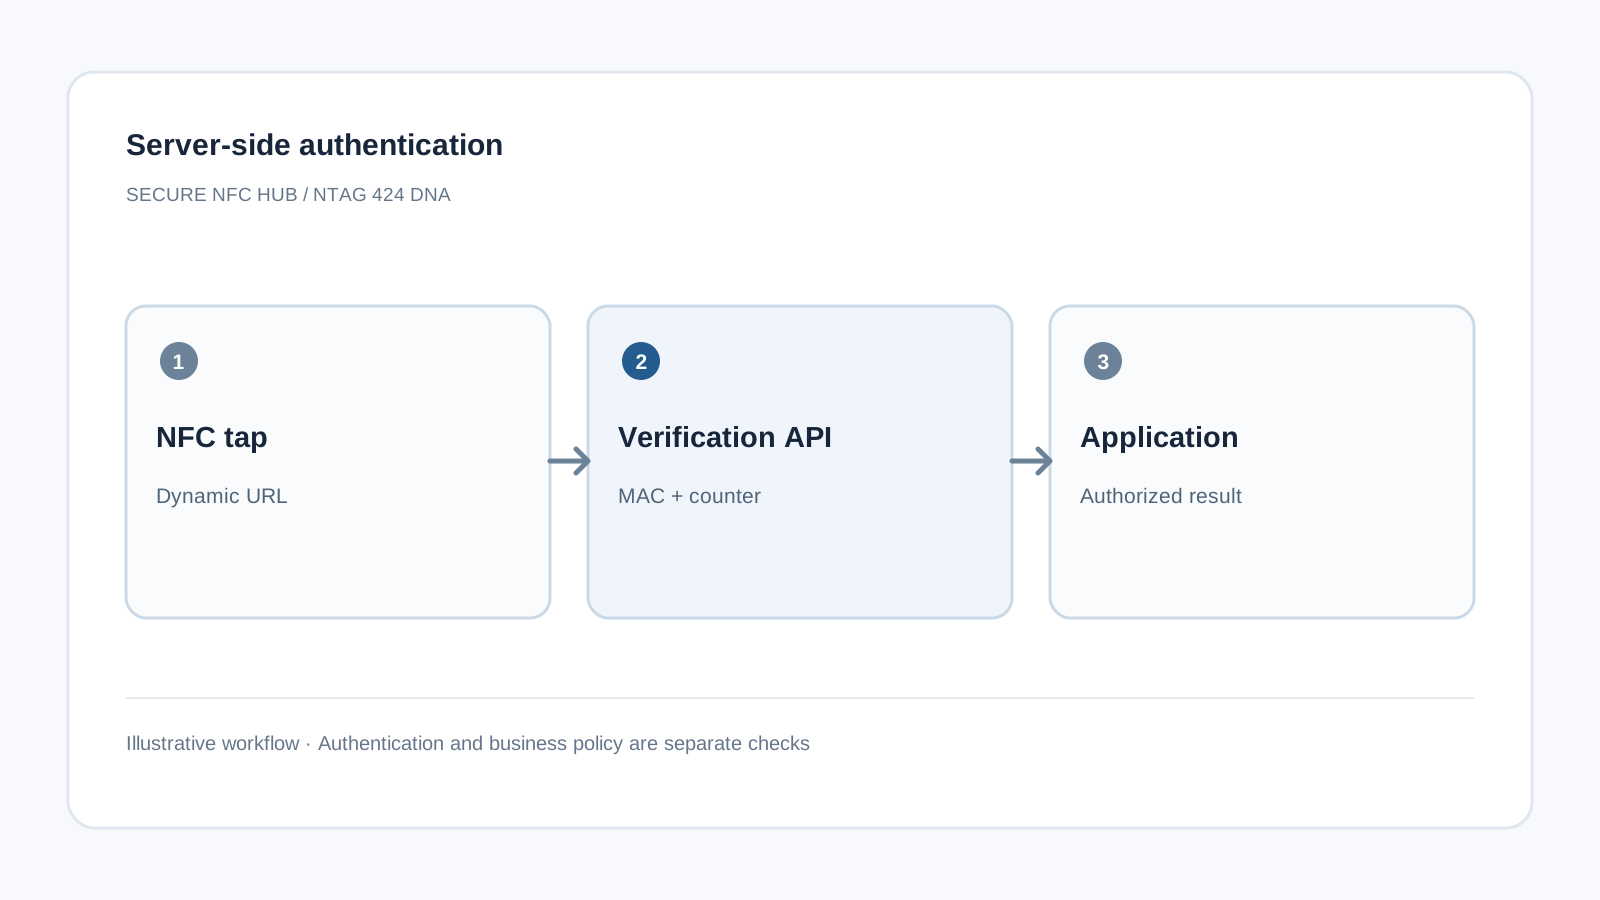
- The phone reads the NTAG424 DNA NDEF URL.
- The application or landing page passes the tap payload to a trusted backend.
- The verifier performs cryptographic checks using protected keys.
- Your business application determines what product information or action to display.
Security architecture
Never embed verification secrets in a public browser application. Enforce transport security, authentication for protected API routes, rate limits, logging and a key rotation plan.
A successful cryptographic check is an input to your product decision, not proof of the contents or ownership of the physical item.
Integration and deployment
- Connect a branded verification page, mobile application or existing product database.
- Agree on response states for valid, invalid, revoked and unrecognized tags.
- Choose managed verification or discuss a deployment within your infrastructure where supported.
- See the platform documentation for the currently documented API interface; exact endpoints and response schemas depend on deployment.
Discuss your API requirements
Share your expected tap volume, hosting preference, backend stack, data residency requirements and whether you already own personalized tags and keys.