01 / CLOUD SECURITY & PROFILES
Secure Issuance
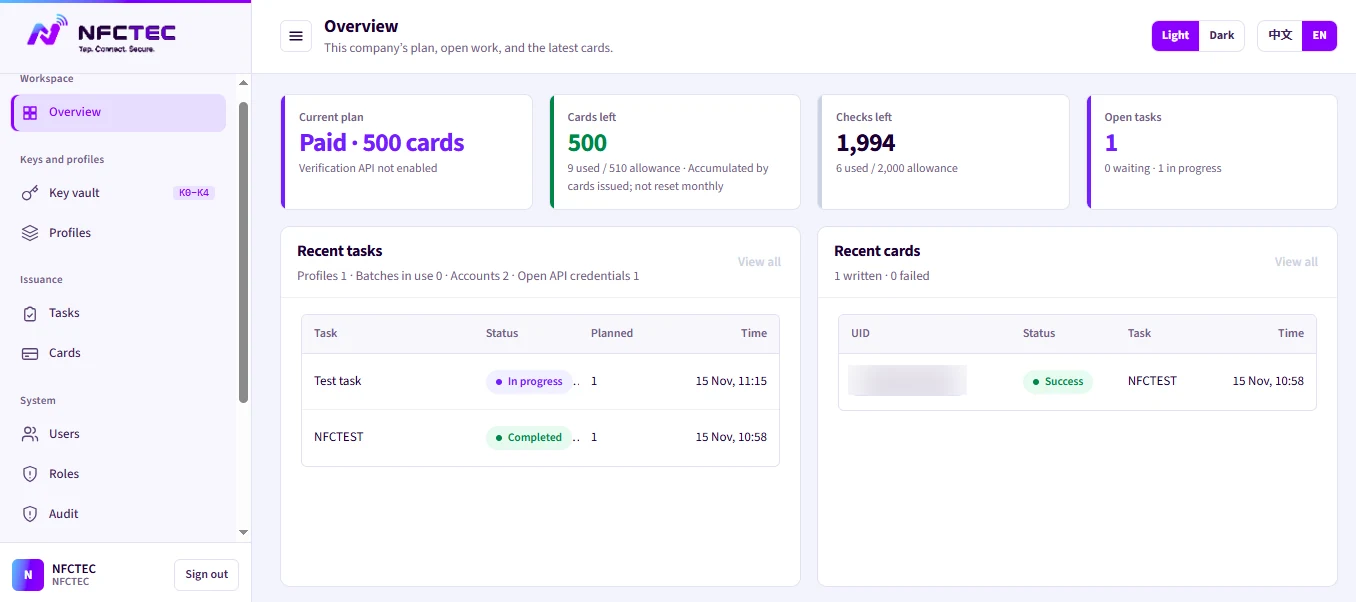
Keep cryptographic processing on the server. Configure KEY0–KEY4, multiple issuance Profiles, file access rules, NDEF URLs and SDM Figure 1, 2 and 4.
Explore secure issuance →MODULE CAPABILITIES
NFCTEC · Enterprise NFC Platform
One connected NTAG 424 DNA system—from cloud-managed personalization to product binding and cryptographic verification.
SERVER-SIDE SECURITY MODEL
Cloud Issuance & Security Engine
AES keys · EV2 sessions · CMAC · Profiles
NFC Clients
Desktop · Android · Apple
No plaintext keys
Business Systems
ERP · Brand App
Bind · Verify · Revoke
Conceptual architecture; not a screenshot of the production console.
Production software
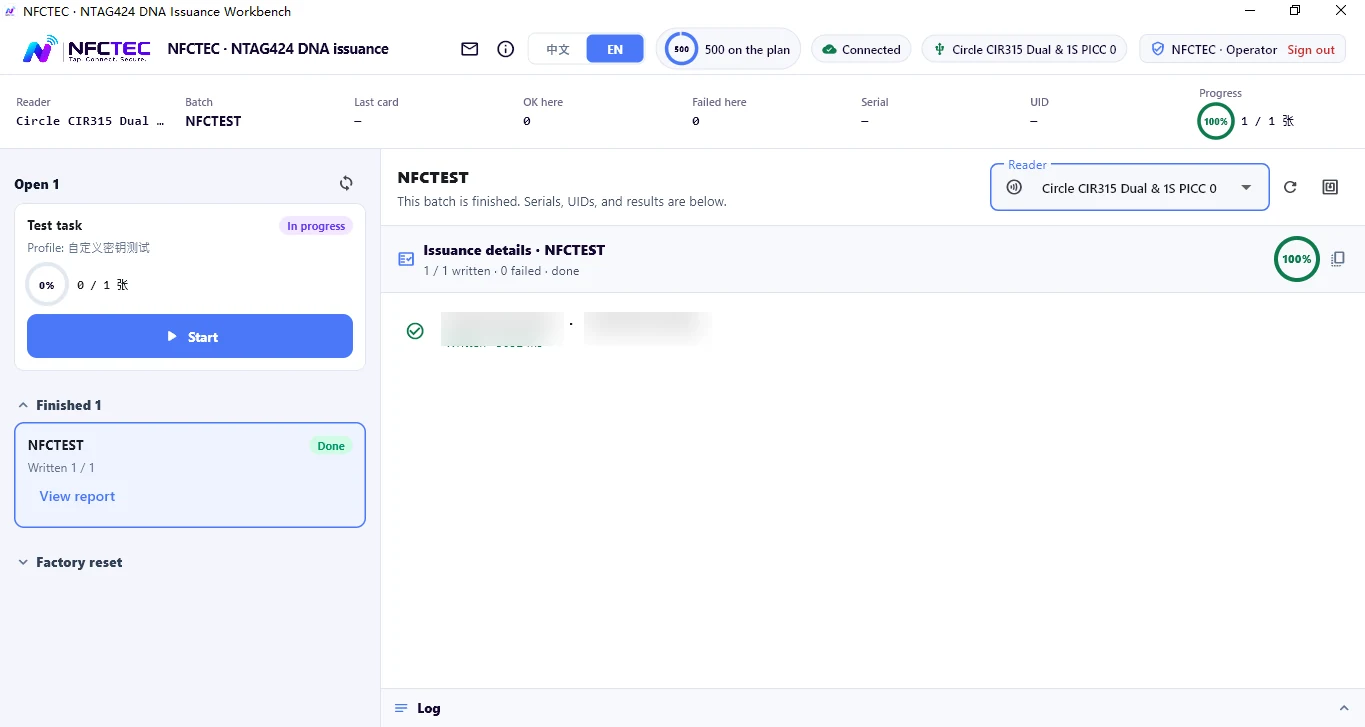
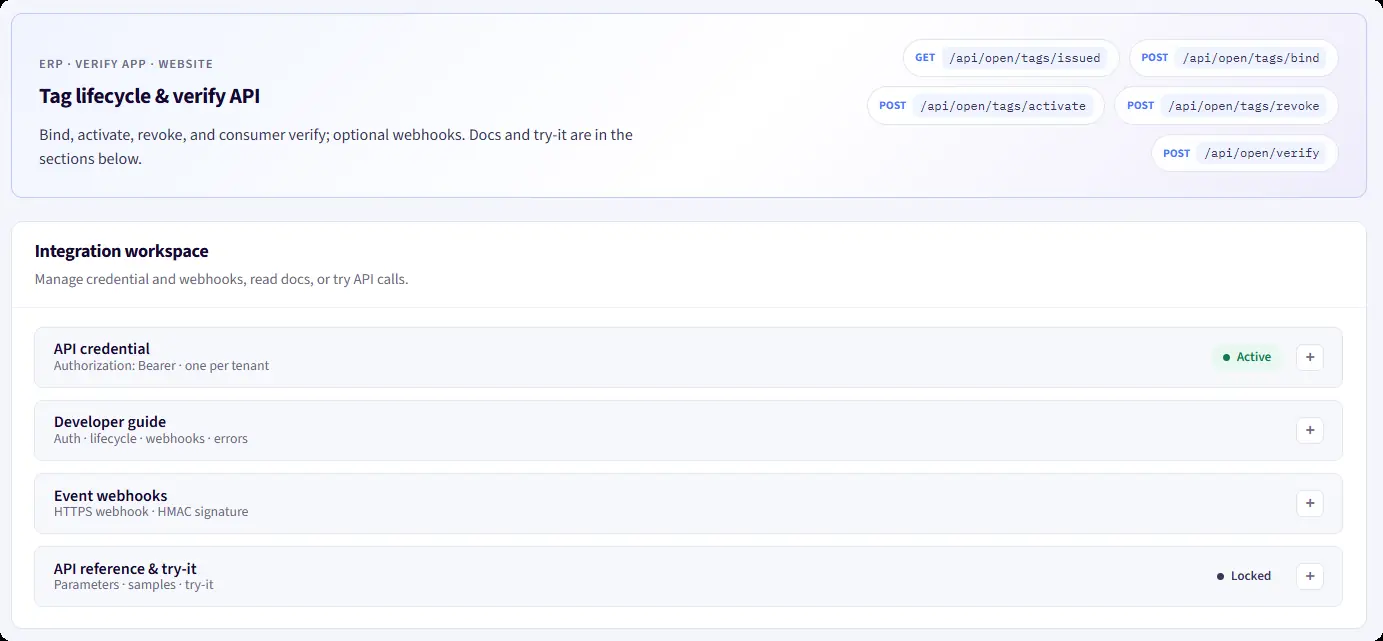
NFCTEC's cloud workspace, PC/SC personalization tool and lifecycle API interface—shown with demonstration data.
Explore module →
Explore module →
Explore module →
Screenshots show demonstration data. Plan status and feature availability shown in screenshots do not represent default customer entitlements.
One connected lifecycle
01
Keys, Profiles, SDM and file access
02
Cloud APDU sessions and issuance tasks
03
Product binding, activation and revocation
04
CMAC, counter and lifecycle checks
Platform modules
Each module is part of the same issuance and authentication platform. Explore the engineering details without losing the end-to-end context.
01 / CLOUD SECURITY & PROFILES
Keep cryptographic processing on the server. Configure KEY0–KEY4, multiple issuance Profiles, file access rules, NDEF URLs and SDM Figure 1, 2 and 4.
Explore secure issuance →MODULE CAPABILITIES
02 / PRODUCTION CLIENTS
Issue cards through task-controlled desktop PC/SC readers, supported Android NFC devices and iPhone or iPad clients. Track successful cards and investigate failures without distributing plaintext keys.
Explore personalization →MODULE CAPABILITIES
03 / VERIFICATION & INTEGRATION
Verify SDM messages with CMAC and replay checks, then apply product registration, activation, revocation and expiry rules. Connect existing business systems through APIs and Webhooks.
Explore authentication API →MODULE CAPABILITIES
Security by design
Issuance clients transport APDU commands and card responses while server-side services perform authentication, EV2 session processing and CMAC calculations. The architecture follows the cloud-personalization model described in NXP AN12196 §8.1.
Cloud-encrypted key storage does not by itself imply HSM-backed cryptographic operations or NXP product certification. Advanced HSM integration remains a roadmap item.
Review the security architecture →Work with NFCTEC
From custom NTAG 424 DNA tags to secure personalization and backend verification. Tell us about your product, packaging, quantity and integration requirements.
Custom hardware Secure issuance Authentication