From physical identity to product record
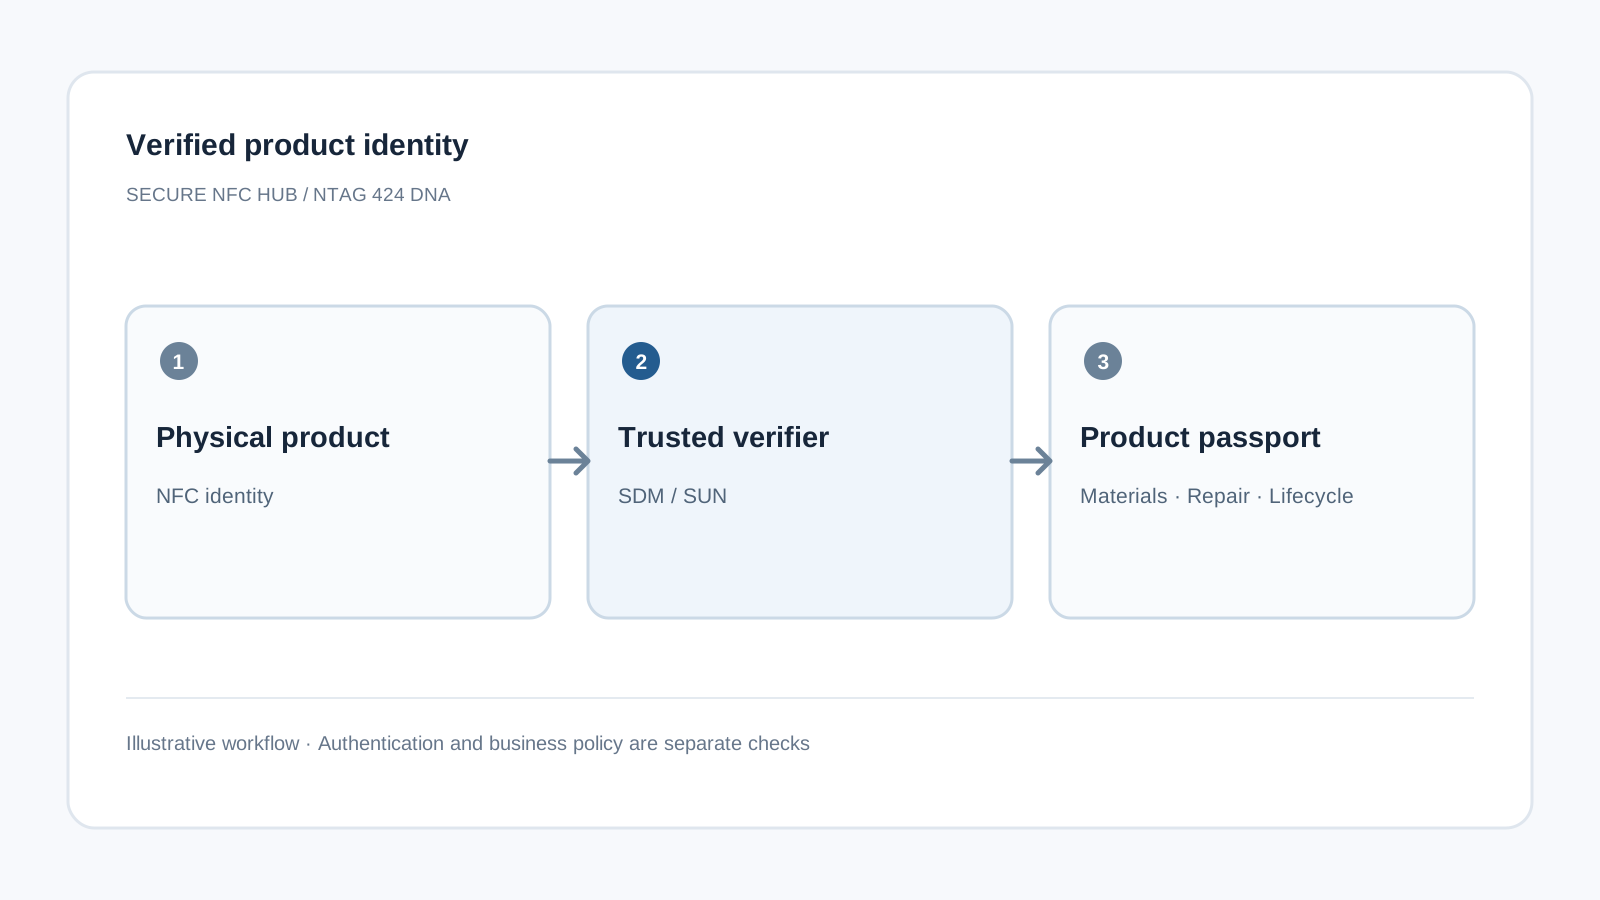
- Issue and register the NFC tag against the correct product identifier.
- Verify the chip-generated SDM/SUN payload through a trusted service.
- Retrieve the relevant passport information from your backend.
- Show permitted content to consumers, service partners or other authorized users.
What belongs in the passport
- Product and manufacturer identifiers
- Materials and care or repair information
- Service and lifecycle events where available
- Relevant recycling or disposal instructions
- Market-specific fields defined by the applicable program
Architecture and data ownership
Keep changeable passport content in your managed systems, not solely in NFC tag memory. Separate cryptographic authentication from access permissions, record accuracy and lifecycle updates.
Regulatory passport requirements vary by product category and jurisdiction. An NFC chip does not itself establish compliance.
Implementation considerations
- Tag durability and placement across the product lifetime
- Stable product identifiers and versioned backend records
- Consumer-accessible pages and partner API access
- Privacy, retention and long-term service availability
Discuss your passport project
Share the product category, expected lifetime, required data fields, systems of record and markets in scope. We can then evaluate the NFC identity and verification layer.