What must be configured
- AES-128 key roles, access conditions and a key-management policy
- NDEF URL template, SDM offsets and enabled dynamic fields
- Issuance profile, batch reference and product binding identifiers
- Verification checks and quality-control records
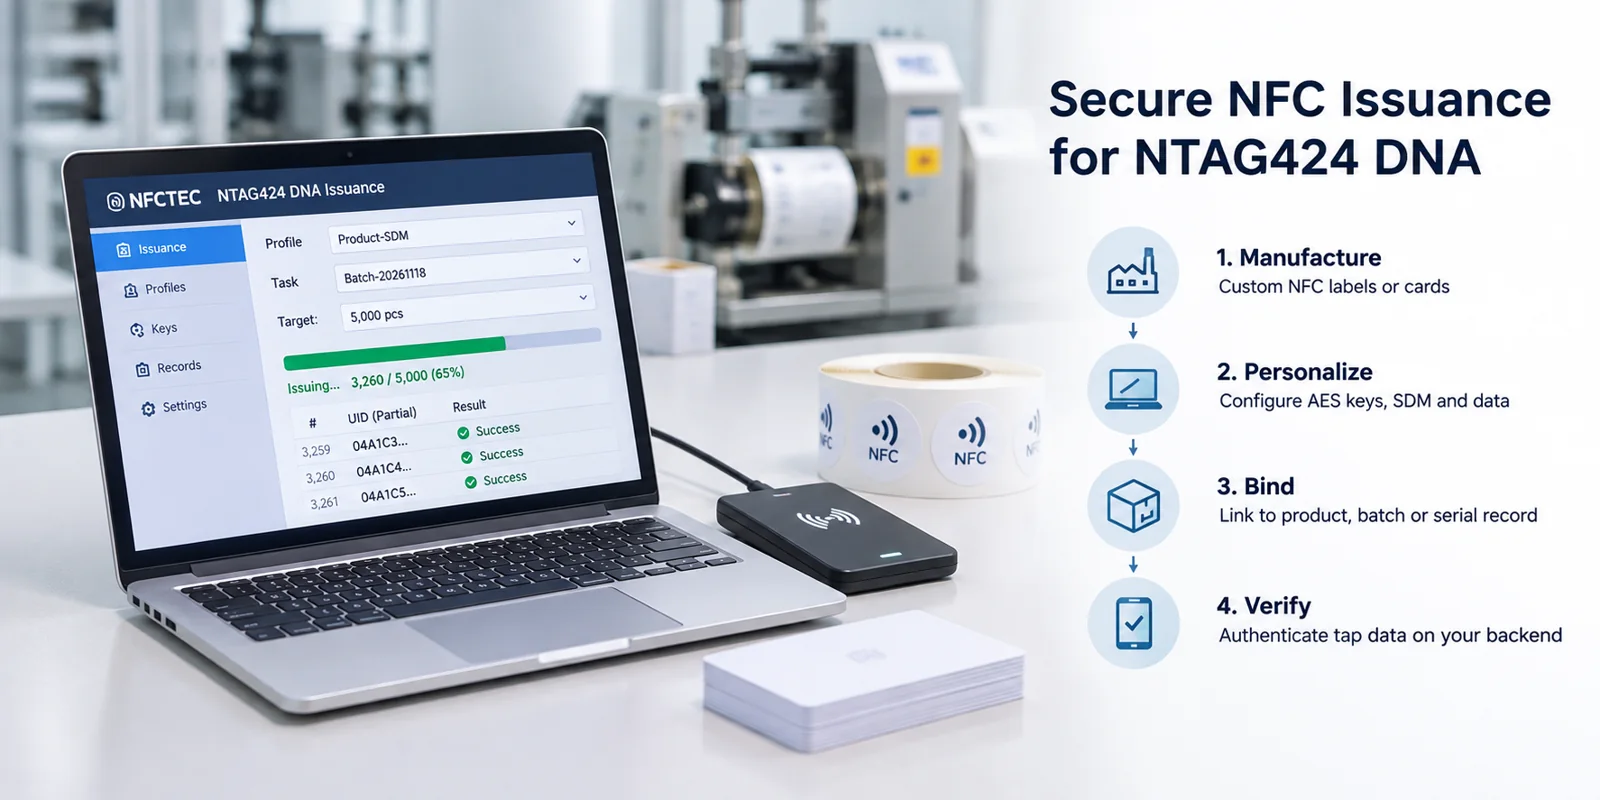
A controlled issuance workflow
- Approve the configuration and sample tags before production.
- Create an authorized issuance batch and select the correct profile.
- Personalize tags using a compatible desktop station or supported cloud-managed workflow.
- Verify written settings and test dynamic URLs against the verifier.
- Export issuance results and reconcile them with manufacturing or product records.
Key management and workstation security
Protect master keys and define how per-tag or per-batch keys are derived where required. Diversification is an issuance-system design decision, not an automatic guarantee of the chip.
In supported server-managed deployments, cryptographic operations can remain server-side while a workstation relays card commands. Deployment details and key custody must be confirmed for each project.
Available integration paths
- Desktop PC/SC personalization and test workflows
- Cloud-managed profiles, issuance tasks and batch tracking
- Verification API integration and product registration
- Independent deployment discussions for suitable enterprise projects
What to specify for a production quote
Provide tag quantity, reader hardware, SDM URL format, key ownership model, required reports and whether issuance happens at the factory or at your site. Do not send production keys through a contact form.